Scaling Access Control
Because individual site-by-site permission management becomes highly inefficient at scale, Awetonet.io utilizes Management Zones.
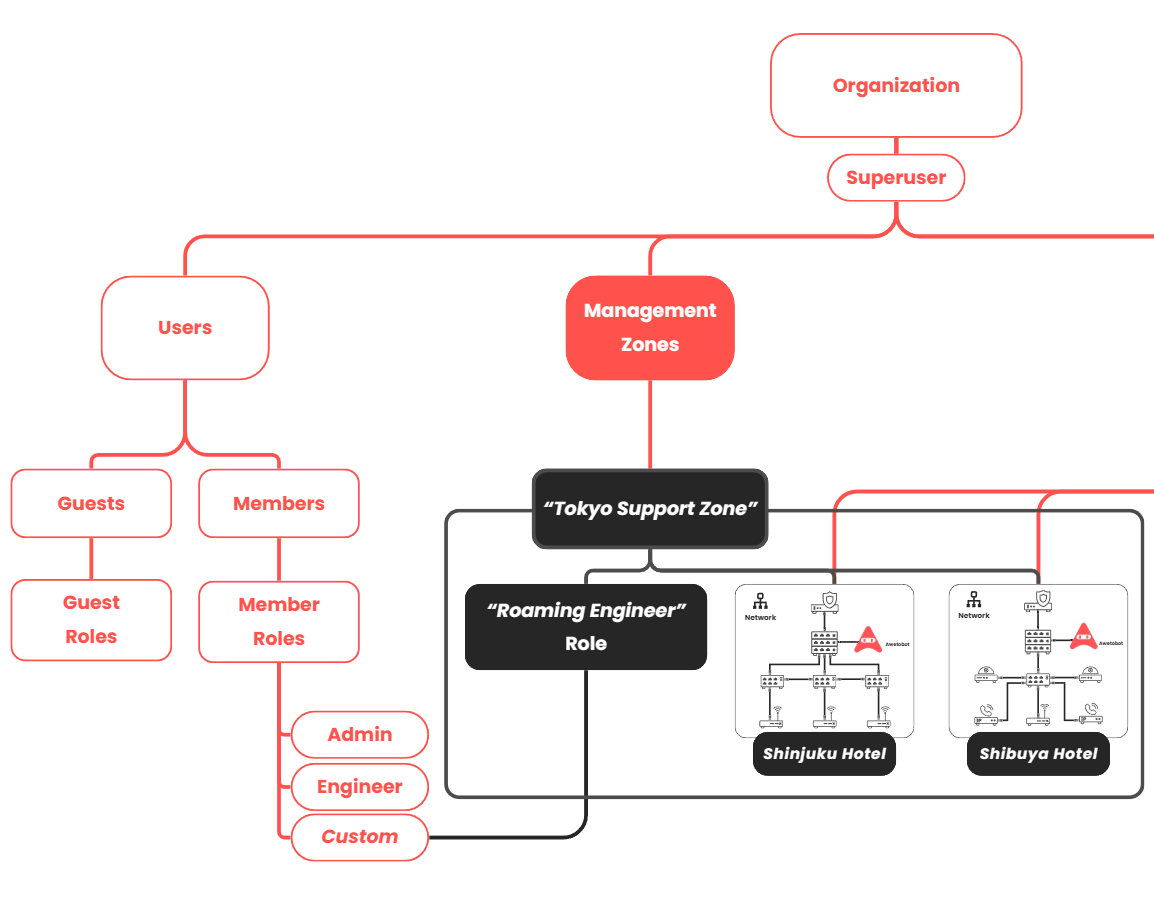
Management Zones are high-efficiency user access templates designed to span infrastructure boundaries and automatically assign corporate user roles to dynamic collections of Sites.
Decoupled Access Architecture
A Management Zone functions as an intermediate logical layer. Instead of assigning a user to a specific physical location, administrators assign roles to a Management Zone, which dynamically applies access permissions across the organization.
- Automated Large-Scale Provisioning: When a new engineer joins the organization, adding them to a single Management Zone automatically grants specific access permissions to multiple relevant Sites simultaneously.
- Cross-Group Flexibility: Since Site Groups are used exclusively for user interface filtering, a single Management Zone can include multiple different Site Groups to align with actual operational requirements.
- Internal Scope Only: Management Zones apply only to internal Members. External third parties (Guests) are excluded from these configuration groups; their access permissions must be reviewed and managed individually for each site.