Security & Multi-Tenant Architecture
Awetonet.io is built from the ground up using a "Defense-in-Depth"(multi-layered) security model. Our architecture ensuring complete isolation between managed client environments, secure data transmission, and zero-knowledge storage principles.
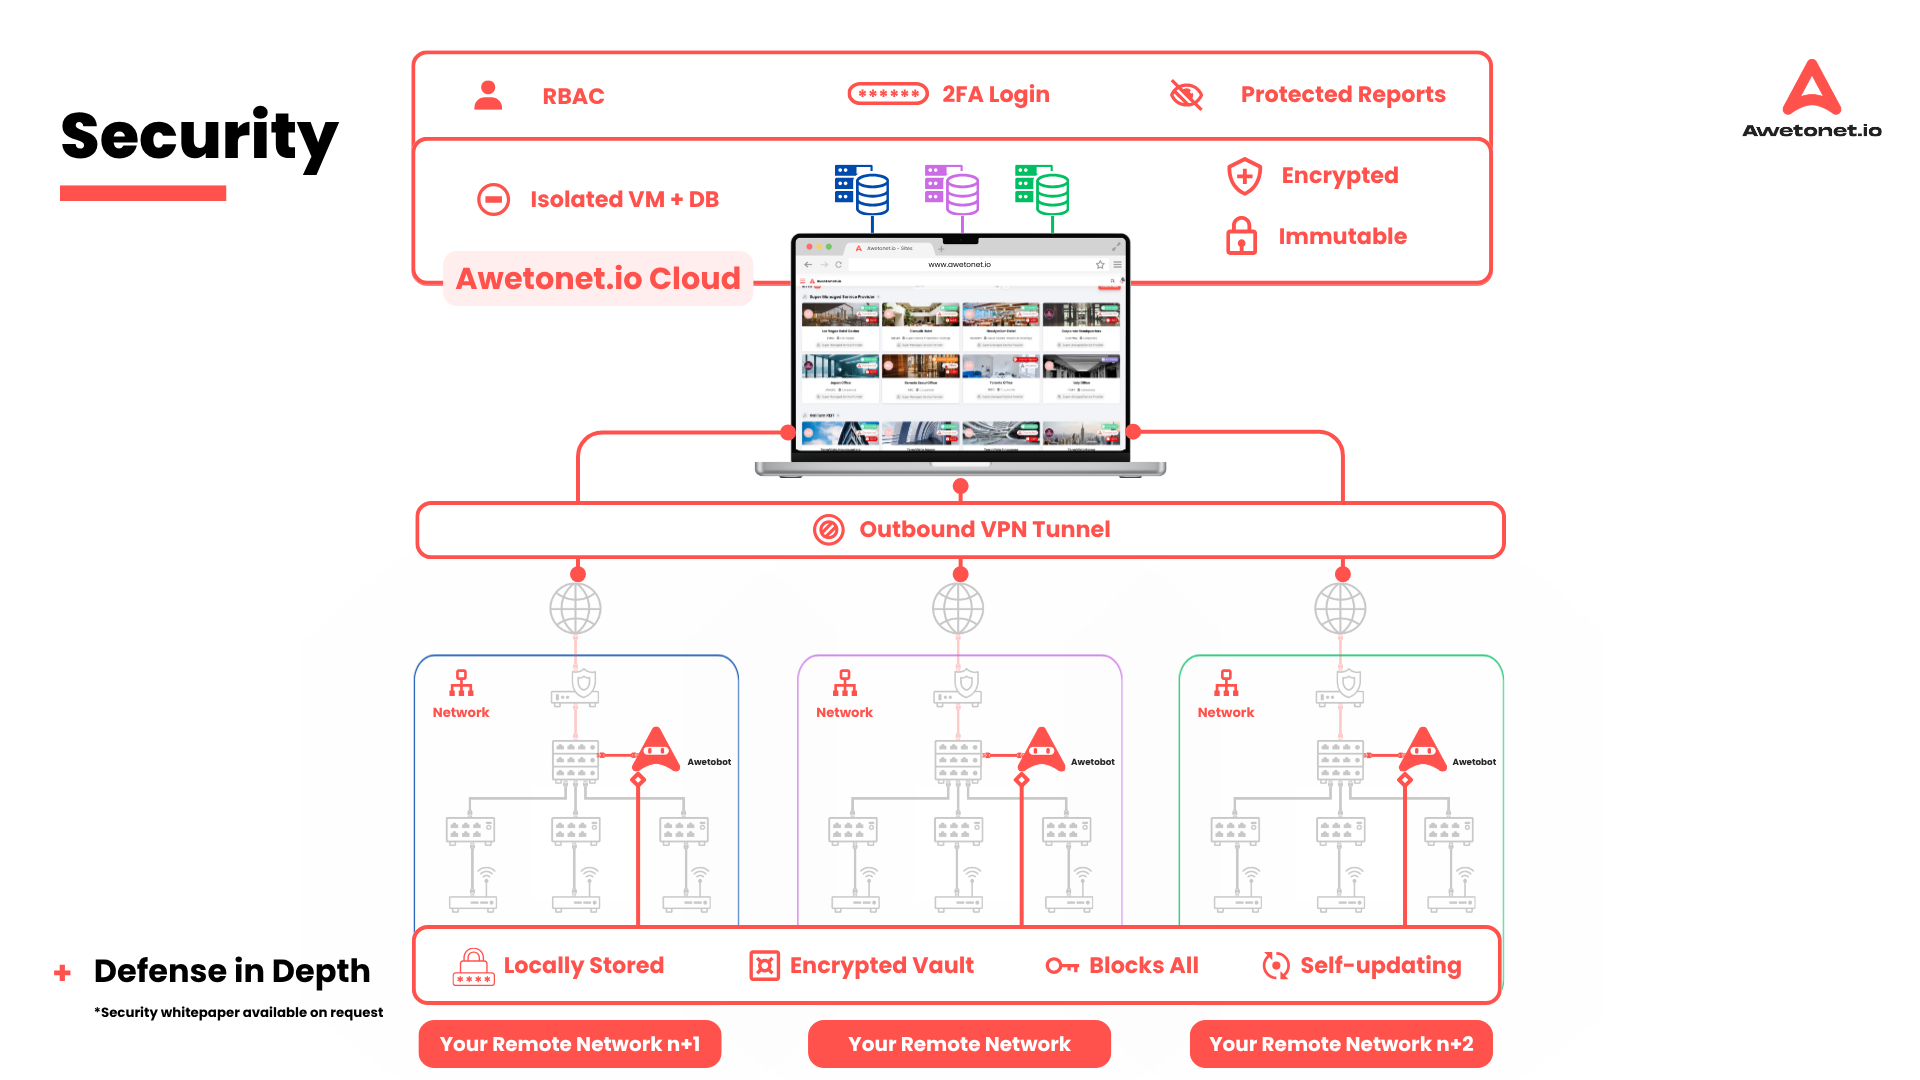
1. Cloud-Layer Security & Tenant Isolation
The Awetonet.io Cloud acts as the central orchestration layer. To protect enterprise data, strict boundaries are enforced at every level:
- Tenant Separation: Client environments are logically separated via isolated virtual machines and dedicated database segmentation. Tenant A cannot query, view, or access Tenant B’s data under any circumstances.
- Access Control: All user access is protected by Role-Based Access Control (RBAC), multi-factor authentication (2FA Login), and strict session management.
- Data Protection: All reporting data, configuration metrics, and logs are encrypted at rest and stored in an immutable format to prevent tampering.
2. Secure Edge Connectivity (The Awetobot Tunnel)
The Awetobot agent communicates with the cloud portal via a dedicated secure tunnel.
- Outbound-Only Communication: The Awetobot initiates a secure VPN tunnel strictly via outbound traffic.
- Zero Open Inbound Ports: There is no requirement to open inbound firewall ports (such as SSH or HTTPS) on the remote network This completely eliminates external perimeter scanning risks.
3. Localized, Zero-Knowledge Credential Storage
To minimize the impact of a potential cloud security incident, network device credentials used for multi-vendor discovery and automation are never stored in plain text in the cloud:
- Encrypted Vault: Device credentials (SSH keys, API tokens, etc.) are encrypted and stored within a secure local vault on the Awetobot.
- Automated Updates: The Awetobot agent uses a secure, automated software update mechanism to ensure it always runs the latest security patches without requiring manual intervention.
🔒 Additional Security Information A comprehensive Security Whitepaper detailing the specific cryptographic ciphers, data-retention policies, third-party penetration test results, and compliance framework mapping is available upon request. Contact a representative to request a copy.